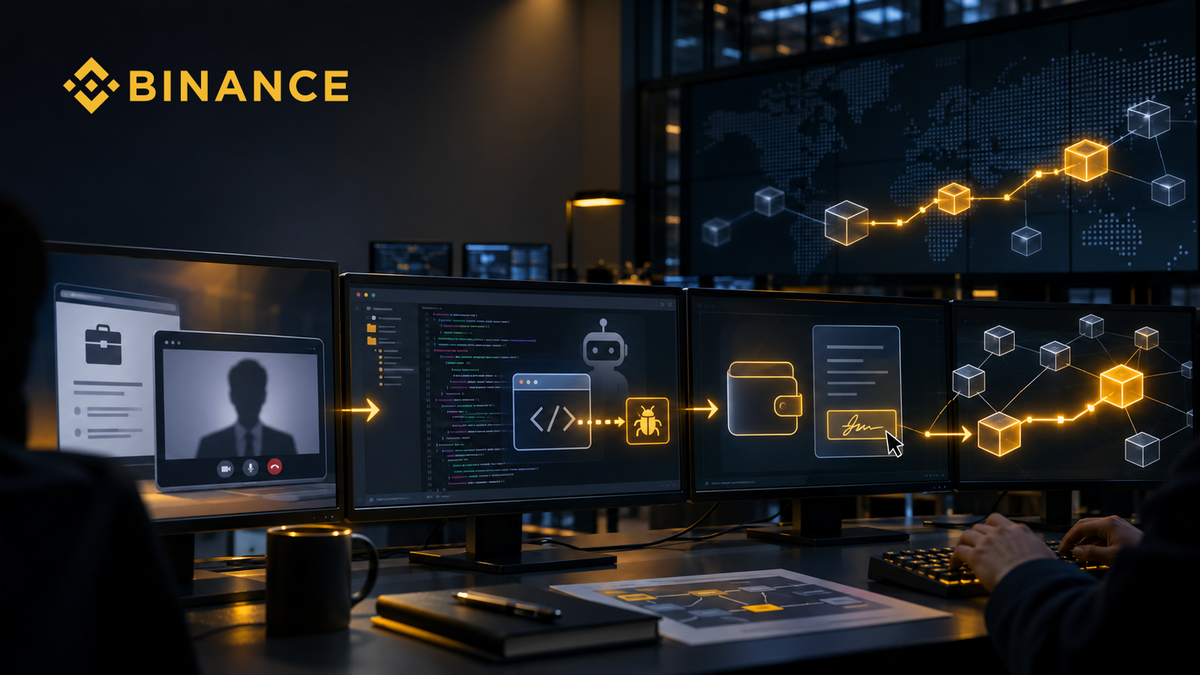
Binance’s first detailed account of the October 29 breach describes a campaign that developed over months rather than a single compromised laptop. According to the exchange, the attackers combined a tampered software installation, a convincing fake recruitment process, zero-day malware, access through an internal AI tool and stolen deployment credentials before reaching wallet-signing operations and abusing EIP-7702 authorisations. Binance estimates that approximately $6.34 billion in digital assets was affected.
Key takeaways
- Binance estimates the incident affected about $6.34 billion and says the company, not users, will absorb the loss.
- The campaign began months earlier with a tampered software download and a separate fake job interview that delivered a malicious code repository.
- The attackers used compromised employee devices, internal AI tooling, deployment credentials and a service container to reach wallet-signing operations.
- Malicious EIP-7702 delegations remained active on-chain, so pausing withdrawals alone could not immediately stop every transfer.
- Binance says 98% of affected token assets had been replenished by October 31, while about $2.85 billion had been frozen or intercepted.
- The findings remain preliminary and are due to undergo independent security review.
What the new report changes
On November 4, 2026, Binance published an initial findings and response report through its official X account. It is the first detailed narrative from the exchange covering the preparation, internal access path, wallet-signing abuse and on-chain containment work.
This is Binance’s preliminary account, not a final independent root-cause report. The company says its investigation remains active, some defensive details will stay confidential and external cybersecurity firms will review the findings.
Binance puts the impact at approximately $6.34 billion. It says more than enough funds have been reserved to cover the loss and that 98% of affected token assets had been replenished by October 31. Separately, approximately $2.85 billion had been frozen or intercepted. Replenishment and recovery are different measures and should not be added together.
The FBI has attributed the incident to North Korea under the TraderTraitor label. SIAMBC’s earlier report covers that attribution and the laundering indicators released by law enforcement.
A campaign months in the making
June: a tampered developer-tool installation
Binance says a Wallet DevOps engineer, identified as Engineer A, downloaded a tampered Homebrew installer while trying to install a popular AI coding tool. The security team detected an anomaly, replaced the device and rotated related credentials. Binance nevertheless believes the incident exposed Engineer A’s role and links to colleagues working on wallet infrastructure.
September: a credible fake recruitment process
Software Engineer B was approached through a legitimate job platform by someone posing as a project director. A live video interview, an apparently established social profile and a second interview with a supposed CEO helped build trust. Near the end of that process, Engineer B was asked to download an assignment containing a malicious code repository onto a work computer.
The malware reportedly replaced a legitimate developer-tool component, contacted an attacker-controlled server and removed traces of its activity. Binance describes it as zero-day malware that the endpoint protection tools in use at the time did not detect.
October 20: internal AI tooling becomes a bridge
According to the report, the attackers used Engineer B’s compromised computer and an internal AI tool to expand access to Engineer A and Software Engineer C. They then discovered a container deployment token stored on Engineer A’s device.
October 29: entry into wallet-signing operations
Between 17:15 and 19:56 UTC, the attackers allegedly accessed Engineer C’s computer, used credentials taken from Engineer A, deployed a container and triggered the malicious script that launched the theft.
Four hours of unauthorised transfers
Between 20:05 and 20:09 UTC, five Binance hot wallets transferred a combined 233.46 million XRP to an attacker-controlled address. Hot wallets on Solana and Optimism also sent approximately 970,500 SOL and 44.2 million OP.
An internal high-volume transfer alert triggered an investigation, but 18,270 BTC was subsequently transferred from a Binance hot wallet. The attackers also used the wallet-signing service to establish malicious EIP-7702 authorisations on Ethereum.
The last unauthorised transfer, 2,961.9 ETH, finalised at 23:56 UTC. Binance says that transaction had already been broadcast and remained pending before it eventually settled while containment work was under way.
Why pausing withdrawals was not enough
EIP-7702 allows an account to delegate limited execution rights to a smart contract without revealing the account’s private key. Binance says the attackers submitted 50 signing transactions to manipulate account nonces and create malicious delegation authorisations. Once recorded on-chain, those permissions could move assets independently of Binance’s normal withdrawal workflow.
That meant suspending withdrawals and shutting down hot-wallet services did not automatically erase the delegations. New on-chain transactions were required to revoke them.
The wallet’s Multi-Party Computation design added operational complexity. There was no single private key that responders could immediately use to revoke the authorisations. Binance developed a specialised MPC procedure and, at 00:10 UTC on October 30, sent a new authorisation from the Binance14 wallet to the zero address to clear the delegation code.
The report does not say that EIP-7702 or Ethereum itself was hacked. The attackers allegedly used access to Binance’s signing process to abuse a legitimate on-chain mechanism.
Containment and recovery
By November 3, Binance said it had rebuilt the affected wallet system and internal AI tooling in new environments, replaced affected devices, decommissioned related credentials and tokens, and completed enhanced scans across employee devices. The company also introduced tighter wallet-service controls and expanded AI-assisted behavioural anomaly detection.
Binance says it is engaging independent security firms, increasing investment in developer-environment and endpoint security, and working on a security research fund and industry initiatives focused on AI security in blockchain environments.
Confirmed findings and open questions
| Question | Status on November 4, 2026 |
|---|---|
| Estimated impact | Approximately $6.34B according to Binance |
| Attribution | The FBI attributes the incident to North Korea’s TraderTraitor activity |
| Was a single laptop the entire cause? | No. Binance now describes a multi-stage path involving several employees and systems |
| Was one private key leaked? | The current account focuses on signing-service access and delegations, not a leaked standalone private key |
| Was 98% of the stolen money recovered? | No. The 98% figure refers to asset replenishment; Binance reports about $2.85B frozen or intercepted |
| Is the investigation complete? | No. These are preliminary findings pending further investigation and independent review |
Lessons for businesses and users
For organisations
- Use approved software repositories and package registries instead of allowing production-linked endpoints to install tools from search results.
- Keep deployment tokens short-lived, narrowly scoped and off employee endpoints whenever possible.
- Treat internal AI tools as privileged systems with device trust, access controls, logging and strict environment separation.
- Maintain an on-chain incident runbook covering approvals, delegations and contract permissions; shutting down an internal service may not revoke existing blockchain permissions.
- Train teams for fake recruitment, deepfake-assisted social engineering and malicious coding assignments.
- Segment wallet signing, deployment and employee productivity environments so one compromised endpoint cannot bridge the entire chain.
For individual users
- The report concerns Binance’s hot-wallet infrastructure; it does not mean every customer account was individually compromised.
- Ignore unsolicited compensation, wallet-verification or recovery links that exploit news of the incident.
- Understand the custody trade-off between leaving assets on an exchange and holding private keys personally.
- A hardware wallet can reduce exchange-custody exposure, but users must still protect the recovery phrase, verify addresses and understand every transaction they approve.
Note: the source report concerns the Binance platform described in its global announcement. It is not evidence that Binance TH was hacked.
FAQ
Did the hack really begin with a fake job interview?
Binance’s initial findings say the fake recruitment process was one part of a broader campaign that also involved a tampered software installation, zero-day malware, internal AI tooling, stolen credentials and a deployment token.
Was EIP-7702 broken?
The report does not identify a vulnerability in EIP-7702. It says the attackers used compromised signing access to create malicious delegations through the mechanism.
Why did MPC not stop the incident immediately?
MPC removes dependence on one standalone private key, but revoking on-chain permissions still required the MPC signing process. Responders could not simply use a single emergency key to clear the delegation.
Will customers bear the loss?
Binance says the company will absorb the financial impact and has reserved more than 100% of the amount required to cover it.
Is this the final technical report?
No. Binance calls it an initial report and says the findings will undergo further investigation and independent review.
References
- Binance: 29 October Security Incident — Initial Findings and Response Update
- Binance Blog: Initial Findings and Response Update
- FBI Cyber Alert
- SANS Internet Storm Center: Tampered Homebrew campaign
Information current to November 4, 2026. The investigation and independent review remain active, and details may change as new evidence is verified. Educational information only; not financial or legal advice.
Share:
FBI attributes $6B+ Binance hack to North Korea’s TraderTraitor